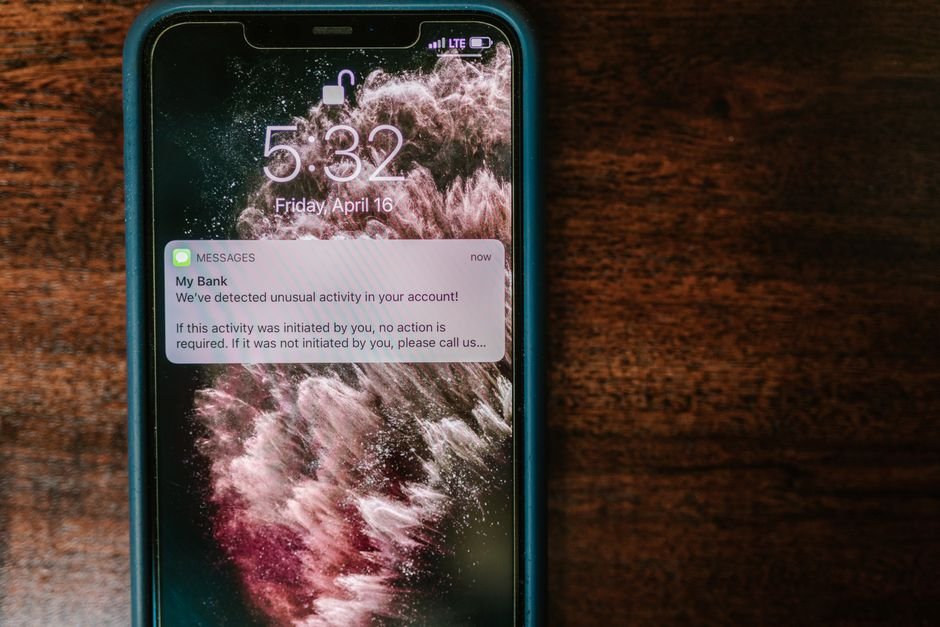
Online fashion retailer Asos has confirmed a security breach after hackers successfully sent unauthorized notifications directly to users of its mobile application. The company acknowledged the compromise following reports from customers who received unexpected and unverified push notifications on their devices, prompting swift cybersecurity reviews and investigative measures across its digital platforms.
The incident involved unauthorized access to the broadcast systems that power push notifications for the Asos mobile app. Bad actors were able to utilize these communication pathways to distribute unauthorized alerts to users. In response, Asos initiated an investigation to isolate the source of the unauthorized activity and ensure that user accounts and core services remained protected.
Key Developments
- Unauthorized Notification Dispatch: Hackers breached communication tools to send unauthorized push notifications directly to Asos mobile app users.
- Official Confirmation: Asos confirmed that the notifications were unauthorized and originated from a security disruption within its app messaging infrastructure.
- Infrastructure Auditing: Technical teams are auditing notification services and access controls to secure system gateways against further intrusions.
Breaches targeting mobile application notification systems highlight critical vulnerabilities in how retail brands manage push communication channels. Asos is working to reinforce its platform safeguards, secure backend protocols, and prevent future unauthorized messages from reaching its global user base.